Please fill out the fields below so we can help you better. Note: you must provide your domain name to get help. Domain names for issued certificates are all made public in Certificate Transparency logs (e.g. crt.sh | example.com), so withholding your domain name here does not increase secrecy, but only makes it harder for us to provide help.
My domain is: bardhome.de
I ran this command: certbot run -a manual -i nginx -d *.bardhome.de
It produced this output:
Saving debug log to /var/log/letsencrypt/letsencrypt.log

Plugins selected: Authenticator manual, Installer nginx

Requesting a certificate for *.bardhome.de

Performing the following challenges:

dns-01 challenge for bardhome.de

- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Please deploy a DNS TXT record under the name
_acme-challenge.bardhome.de with the following value:
ODSRq86u-jtw1UoqMsfEpNOnMNjFM4DfuOJD_HGeUmM
Before continuing, verify the record is deployed.
- - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - - -
Press Enter to Continue
Waiting for verification...
Challenge failed for domain bardhome.de
dns-01 challenge for bardhome.de
Cleaning up challenges
Some challenges have failed.
My web server is (include version): nginx container for docker
The operating system my web server runs on is (include version): ubuntu 20
My hosting provider, if applicable, is: none
I can login to a root shell on my machine (yes or no, or I don't know): yes
I'm using a control panel to manage my site (no, or provide the name and version of the control panel): no
######################################
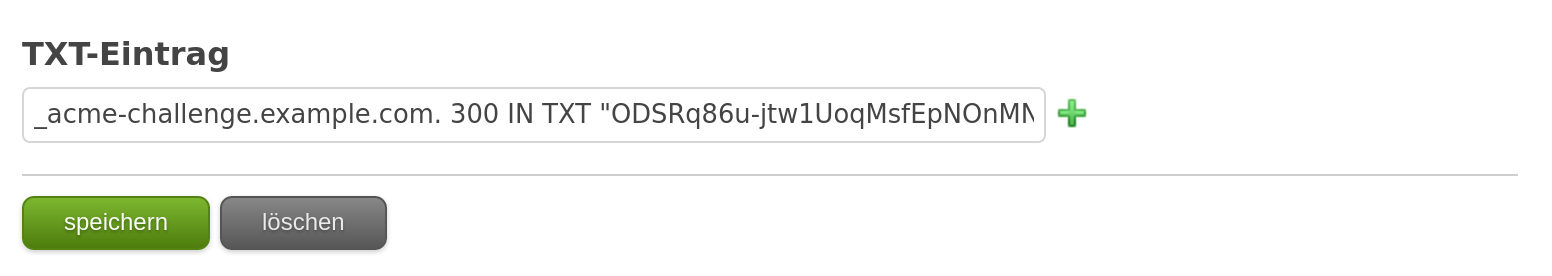
I entered the following text to my dns record at domainssaubillig.de:
_acme-challenge.example.com. 300 IN TXT "ODSRq86u-jtw1UoqMsfEpNOnMNjFM4DfuOJD_HGeUmM"
When I do the challenge for the subdomains manually (so no wildcard, but single domains p.ex. test.bardhome.de, subdomain.bardhome.de), its works. But I like to use the wildcard.